


1. In the Policy information view in Aranda Security Compliance, on the Groups You will be able to view the list of groups associated with the policy, along with the number of devices in each group.
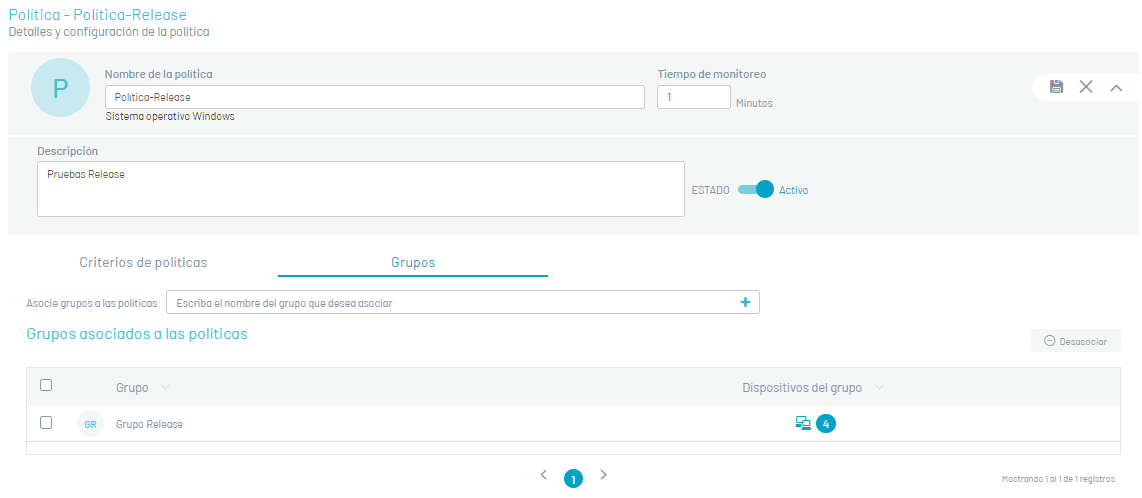
2. To check the compliance detail of the devices in a group, go to the Configuration > Compliance Groupsicon, and select the device icon from the required group. The window is enabled Devices with the related information of the associated devices: name, operating system, IP, execution date and remediation action to be executed according to the level of compliance of the group.
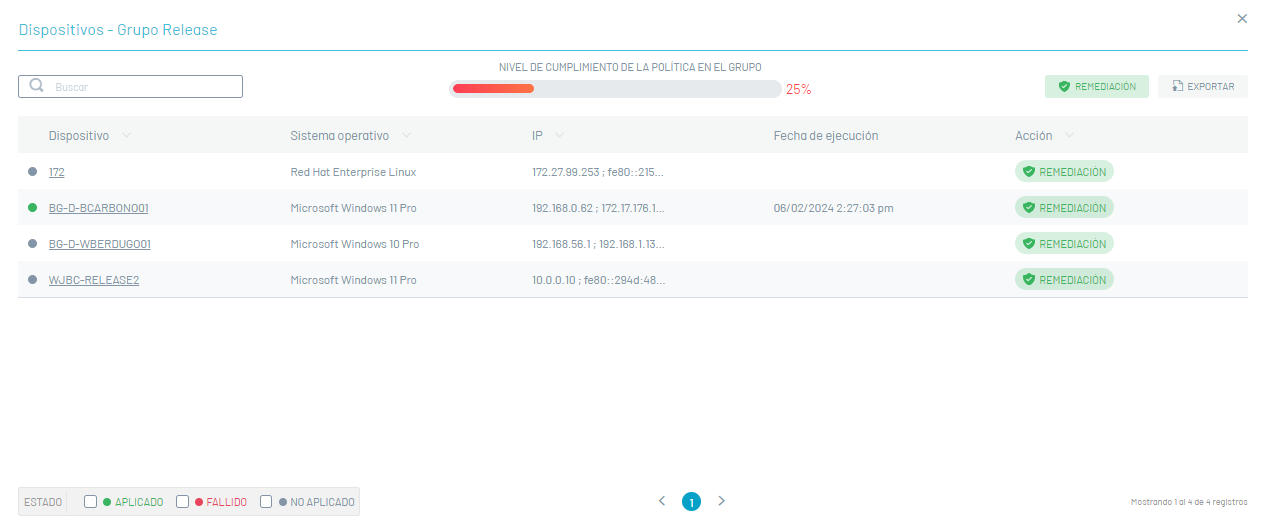
3. Selecting the device name opens the device detail page, where you can view the vulnerability summary and, using the tabs Policies, Groups, Vulnerabilities and Remediation Activity, the information related to device compliance.
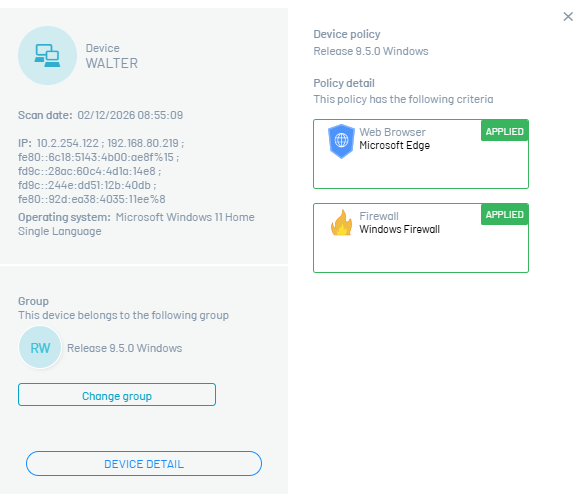
4. The detail of the policy applied to the device will be able to visualize the level of compliance with the criteria of the implemented policies, through the referenced States:
| States | Description |
|---|---|
| Successful | The Successful status is displayed when the policy criterion is met, applied to the device. |
| Failed | The failed status is displayed when the policy criterion, applied to the device, is NOT met |
| Not Applicable | The Not Applicable status is displayed when the device has not been scanned. |
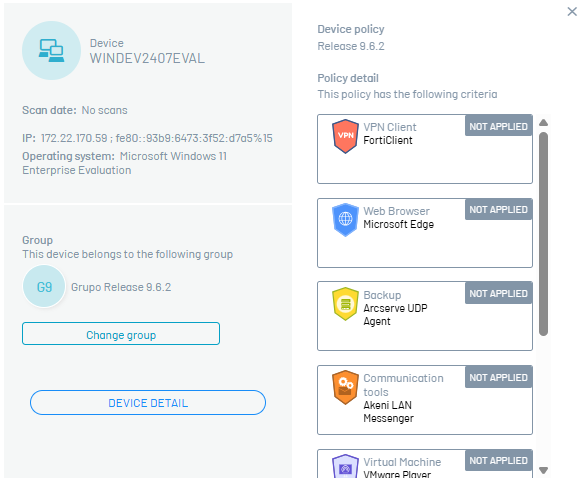
5. On the Policies From the device detail, each policy criterion is displayed on an expandable card; when unfolded, individual validations are displayed with their respective status.
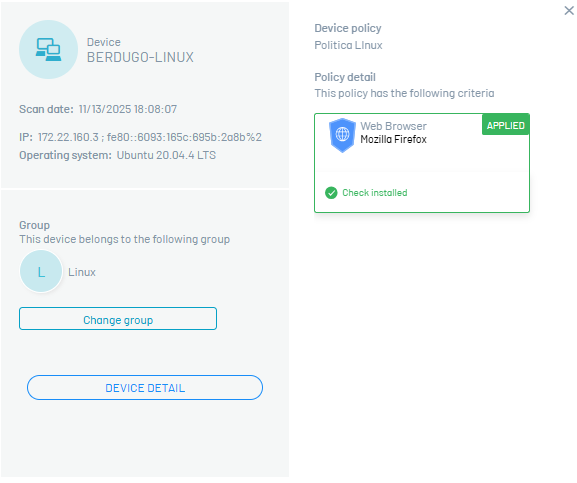
⚐ Note: The full device detail is displayed directly when selecting the device name; an additional “Device Detail” button is not required.
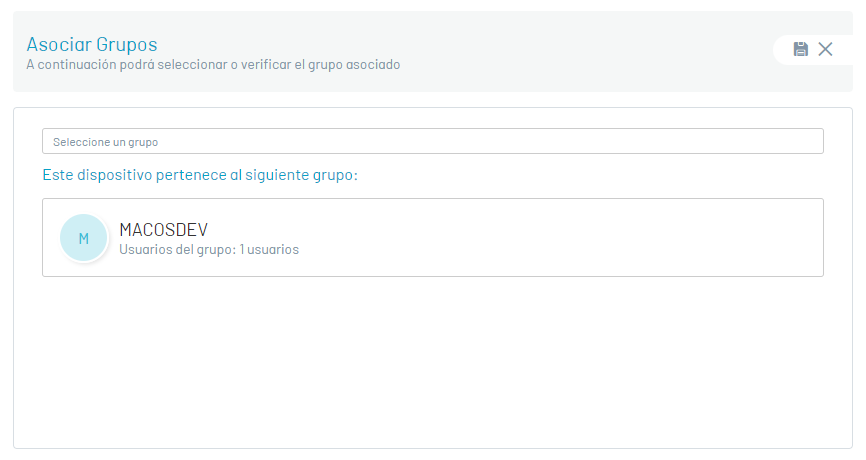
⚐ Note: On the Groups from the device detail, select the Change Group to modify the existing group association.
Remediation Actions
6. Regardless of the status generated (Successful, Failed, or Not Applicable) during the policy compliance analysis on the devices, you will be able to execute the required remediation actions. Select the Remediation to execute the actions enabled for the implemented security criterion.
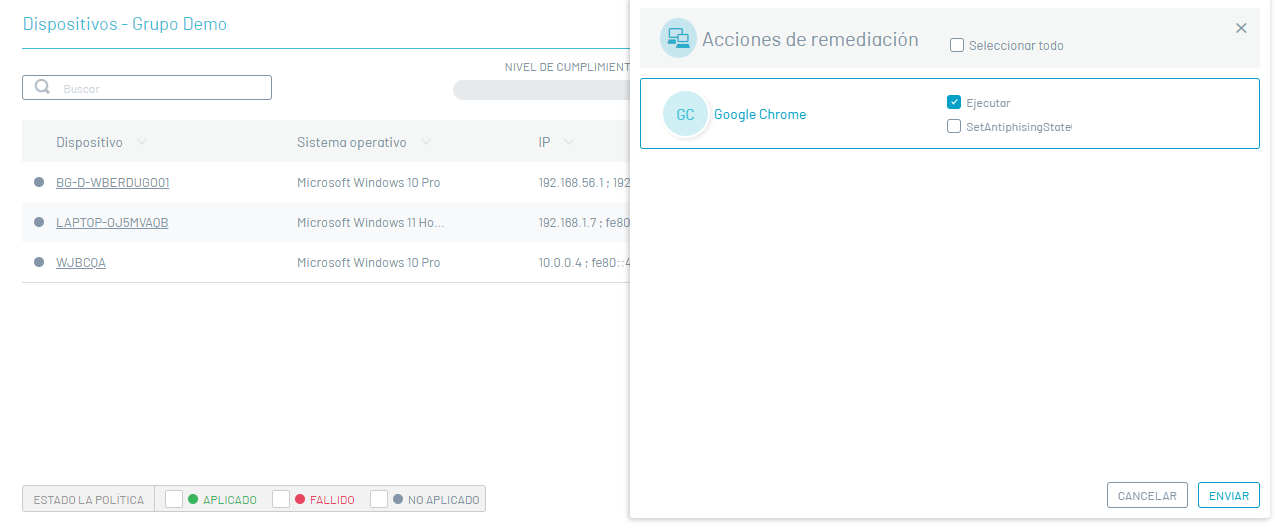
⚐ Note: When you select the Save The chosen remediation actions will be implemented.
7. In the window Remediation Actions, each detected criterion (Antimalware, Firewall, VPN Client, and others) shows the available actions based on the program type, such as Scanning, Set agent status or Enable ransomware protection.
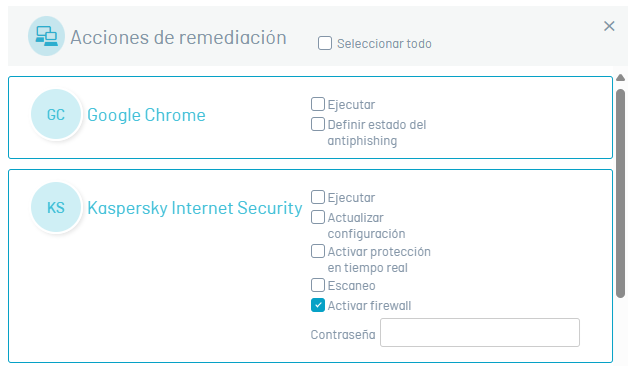
⚐ Note: In this window, remediation actions do not prompt for an admin password; actions are executed directly with the permissions of the agent installed on the device.